Win 7 Security Cleaner Pro is a fraud which pretends to be a legitimate and professional antivirus program to cheat users.
Once infiltrating into your computer completely, it starts to scan the computer without your permission and then shows you a list of dangerous threats on the scan result. In fact, those threats are nonexistent.
Win 7 Security Cleaner Pro aims at convincing you that your computer is in a high-risk condition and you shall purchase its full version to fix the computer. It is able to take control of your computer preventing you from running web browsers or any other programs in the computer. In such condition, you may think that there is no other choice except paying to it. Actually, your computer will still be infected even if you pay to the cyber criminals who designed this virus for what they want is more and more money. This Win 7 Security Cleaner Pro Virus should be removed from your computer immediately.
Monday, 18 March 2013

Friday, 24 August 2012
Isearch.claro-search Virus Removal Help
Isearch.claro-search Virus is a latest malicious browser hijacker that makes great chaos to your computer. Remote hackers are able to connect to your computer with the help of some backdoor Trojans. Those are probably attached in the advertisement page where Isearch.claro-search Virus redirects you. Since Isearch.claro-search Virus is able to change system settings and add malicious registries, every time you boot the computer, Isearch.claro-search Viruswill begin to “work”. Even when you reboot the computer and get in the safe mode with networking, this Isearch.claro-search Virusstill “haunts” on the computer. Some computer experts said this Isearch.claro-search Virusonly wants to sell its associate program. If users leave this Isearch.claro-search Virus in the computer, they may keep receiving annoying message like: "WARNING! Your computer is infected with spyware!" or “PC is at high-level risk!” Problems have been posted everywhere and you can find so much information about this Isearch.claro-search Virus. This article is just posting roughly content about this hijacker, we will sincerely provide you useful and the most effective guide in following and Good luck. This Isearch.claro-search Virus should be removed from your computer immediately.
Wednesday, 1 August 2012
Trojan Horse Dropper.Generic_C.MMI Removal
Trojan Horse Dropper.Generic_C.MMI is a latest malicious Trojan horse that makes great chaos to your computer. The word “Trojan” dates from the myth of ancient Greek, Trojan horse comes from a famous story-Trojan War. In computer terms, is a malware,“Trojan” program is the popular virus like this Trojan Horse Dropper.Generic_C.MMI. Nowadays, they differ from the ordinary virus, they doesn’t reproduce themselves and infect other files on purpose. They often disguise themselves as harmless and beneficial programs but instead have a hidden purpose that you are unaware of. Being different with Teamviewer, “Trojan” is malicious, hidden program that control your computer in order to steal your important information. They control another computer via some special programs (Trojan Horse Dropper.Generic_C.MMI), they usually run by two executable programs: one is client, the other is server. The so-called “hacker” access into the computer which is operating the server by taking advantage of the controller. In common word, Trojan operates in backstage by stealing users’ information but the users unaware of them. This Trojan Horse Dropper.Generic_C.MMI should be removed from your computer immediately.
2. Your files on the computer such as .HTML and other executable format may have been infected with Trojan Horse Dropper.Generic_C.MMI.
3. Registry settings and background of infected computer will be changed and search browsers are redirected without notification
4. Your computer performs very slowly and may be frozen easily once suffered from Trojan Horse Dropper.Generic_C.MMI.
5. Trojan Horse Dropper.Generic_C.MMI will change your desktop icons, homepages or Toolbars without your permission.
6. Some nasty pop-ups or a dozen of commercial ads will show on your screen when you search on the Internet.
7. Sometimes you would find that your personal data is stole by Trojan Horse Dropper.Generic_C.MMI.
Step 2: Press CTRL+ALT+DEL or CTRL+SHIFT+ESC. Open the Windows Task Manager and Delete associated files from your PC completely as follows:
%AllUsersProfile%\ApplicationData\~
%AllUsersProfile%\ApplicationData\~r
%AllUsersProfile%\ApplicationData\.dll
%AllUsersProfile%\Application Data\.exe
Step 3:Remove malicious files related to Trojan Horse Dropper.Generic_C.MMI
Malicious registry entries:
HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\MiNODLogin HKCU\SOFTWARE\CLASSES\CLSID\ HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\Run
Step 4: Reboot your computer to normal mode after you have done all steps above.
Trojan horse like Trojan Horse Dropper.Generic_C.MMI can get the right of using the computer without users’ permission. The capacity of this program is very small, they won’t take much more recourses when they are working, so as is hard to be detected if you don’t install any anti-virus software, you are easy to get infected with Trojan Horse Dropper.Generic_C.MMI. When they are working, is difficult to stop them, after working, they will auto-login in the Boot, and after that every time when Windows is loading they will working automatically; otherwise, system will change the filename automatically immediately, or hidden; or even copy to other folder, operating the system even users cannot do. Trojan Horse Dropper.Generic_C.MMI installed, which the hacker can then use to control the target computer.
If the computer is hacked by Trojan Horse Dropper.Generic_C.MMI, our information will be threatened. They will steal our online account, threat our virtual properties and get profit from them. Also our E-bank information, which Trojan Horse Dropper.Generic_C.MMI uses the keyboard or other ways to steal our real properties. Trojan use communication software to steal our identities thus spread the Trojan Horse Dropper.Generic_C.MMI virus. They will open our computer’s backstage, so as that our pc might be controlled by hackers.
Note: If you failed to remove Trojan Horse Dropper.Generic_C.MMI virus with the method above, please consult PC experts to remove it completely.
Symptoms to Judge Your Computer has been Infected by Trojan Horse Dropper.Generic_C.MMI
1. The Trojan Horse Dropper.Generic_C.MMI installs some malicious types of malwares or spywares into your computer without your permission.2. Your files on the computer such as .HTML and other executable format may have been infected with Trojan Horse Dropper.Generic_C.MMI.
3. Registry settings and background of infected computer will be changed and search browsers are redirected without notification
4. Your computer performs very slowly and may be frozen easily once suffered from Trojan Horse Dropper.Generic_C.MMI.
5. Trojan Horse Dropper.Generic_C.MMI will change your desktop icons, homepages or Toolbars without your permission.
6. Some nasty pop-ups or a dozen of commercial ads will show on your screen when you search on the Internet.
7. Sometimes you would find that your personal data is stole by Trojan Horse Dropper.Generic_C.MMI.
Manual Removal is the Best Way to Remove Trojan Horse Dropper.Generic_C.MMI.
Step 1: restart your infected computer into Safe Mode with Networking: Restart your computer. As your computer restarts but before Windows launches, tap "F8" key constantly. Use the arrow keys to highlight the "Safe Mode with Networking" option, and then press ENTER.Step 2: Press CTRL+ALT+DEL or CTRL+SHIFT+ESC. Open the Windows Task Manager and Delete associated files from your PC completely as follows:
%AllUsersProfile%\ApplicationData\~
%AllUsersProfile%\ApplicationData\~r
%AllUsersProfile%\ApplicationData\.dll
%AllUsersProfile%\Application Data\.exe
Step 3:Remove malicious files related to Trojan Horse Dropper.Generic_C.MMI
Malicious registry entries:
HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\MiNODLogin HKCU\SOFTWARE\CLASSES\CLSID\ HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\Run
Step 4: Reboot your computer to normal mode after you have done all steps above.
Trojan horse like Trojan Horse Dropper.Generic_C.MMI can get the right of using the computer without users’ permission. The capacity of this program is very small, they won’t take much more recourses when they are working, so as is hard to be detected if you don’t install any anti-virus software, you are easy to get infected with Trojan Horse Dropper.Generic_C.MMI. When they are working, is difficult to stop them, after working, they will auto-login in the Boot, and after that every time when Windows is loading they will working automatically; otherwise, system will change the filename automatically immediately, or hidden; or even copy to other folder, operating the system even users cannot do. Trojan Horse Dropper.Generic_C.MMI installed, which the hacker can then use to control the target computer.
If the computer is hacked by Trojan Horse Dropper.Generic_C.MMI, our information will be threatened. They will steal our online account, threat our virtual properties and get profit from them. Also our E-bank information, which Trojan Horse Dropper.Generic_C.MMI uses the keyboard or other ways to steal our real properties. Trojan use communication software to steal our identities thus spread the Trojan Horse Dropper.Generic_C.MMI virus. They will open our computer’s backstage, so as that our pc might be controlled by hackers.
Note: If you failed to remove Trojan Horse Dropper.Generic_C.MMI virus with the method above, please consult PC experts to remove it completely.
Saturday, 21 July 2012
How to Remove Trojan.sirefef.HK Step by Step?
Trojan.sirefef.HK is a latest malicious Trojan horse that makes great chaos to your computer and compromise the security of target computer system. It installs other types of malicious applications and modifies your system in many ways without your permission. It changes the registry entries settings and download some other malicious files on the infected system, changes your desktop image, homepage and many important computer settings randomly. Trojan.sirefef.HK sneaks into your computer secretly when you visit some malicious contents or download free items from infected websites unwarily, and then traces your browser habits and system resource to steal information from your infected system and sent it to remote attackers. Trojan.sirefef.HK can also attach some strange email attachments, which contains an executable file. Once be infected by Trojan.sirefef.HK, your computer may performs very slowly and may be frozen easily. This Trojan horse should be removed from your computer immediately.
2. Your files on the computer such as .HTML and other executable format may have been infected. 3. Registry settings and background of infected computer will be changed and search browsers are redirected without notification
4. Your computer performs very slowly and may be frozen easily.
5. It will change your desktop icons, homepages or Toolbars without your permission.
6. Some nasty pop-ups or a dozen of commercial ads will show on your screen when you search on the Internet.
7. Sometimes you would find that your personal data is stole
Step 2: Press CTRL+ALT+DEL or CTRL+SHIFT+ESC. Open the Windows Task Manager and Delete associated files from your PC completely as follows: %AllUsersProfile%\ApplicationData\~ %AllUsersProfile%\ApplicationData\~r %AllUsersProfile%\ApplicationData\.dll %AllUsersProfile%\Application Data\.exe malicious registry entries: HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\MiNODLogin HKCU\SOFTWARE\CLASSES\CLSID\ HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\Run
Step 3:Remove malicious files related to Trojan.sirefef.HK
C:\Windows\System32\services.exe
C:\Windows\System32\drivers\str.sys
C:\Windows\SysWOW64\drivers\str.sys
Step 4: Reboot your computer to normal mode after you have done all steps above. Note: If you failed to remove Trojan.sirefef.HK virus with the method above, please consult PC experts to remove it completely.
Symptoms to Judge Your Computer has been Infected byTrojan.sirefef.HK
1. The virus installs some malicious types of malwares or spywares into your computer without your permission.2. Your files on the computer such as .HTML and other executable format may have been infected. 3. Registry settings and background of infected computer will be changed and search browsers are redirected without notification
4. Your computer performs very slowly and may be frozen easily.
5. It will change your desktop icons, homepages or Toolbars without your permission.
6. Some nasty pop-ups or a dozen of commercial ads will show on your screen when you search on the Internet.
7. Sometimes you would find that your personal data is stole
Manual Removal is the Best Way to Remove Trojan.sirefef.HK.
Step 1: restart your infected computer into Safe Mode with Networking: Restart your computer. As your computer restarts but before Windows launches, tap "F8" key constantly. Use the arrow keys to highlight the "Safe Mode with Networking" option, and then press ENTER.Step 2: Press CTRL+ALT+DEL or CTRL+SHIFT+ESC. Open the Windows Task Manager and Delete associated files from your PC completely as follows: %AllUsersProfile%\ApplicationData\~ %AllUsersProfile%\ApplicationData\~r %AllUsersProfile%\ApplicationData\.dll %AllUsersProfile%\Application Data\.exe malicious registry entries: HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\MiNODLogin HKCU\SOFTWARE\CLASSES\CLSID\ HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\Run
Step 3:Remove malicious files related to Trojan.sirefef.HK
C:\Windows\System32\services.exe
C:\Windows\System32\drivers\str.sys
C:\Windows\SysWOW64\drivers\str.sys
Step 4: Reboot your computer to normal mode after you have done all steps above. Note: If you failed to remove Trojan.sirefef.HK virus with the method above, please consult PC experts to remove it completely.
Saturday, 18 February 2012
Remove Antivirus Protection 2012 Virus Manually
What is Antivirus Protection 2012?
Antivirus Protection 2012 is a new released fake antivirus designed by hackers who want to use the virus to control your computer. Antivirus Protection 2012 is a rogue anti-virus program and has nothing to do with securing your computer even if it acts as it is legit software. The present IT world is indeed overwhelmed with plenty of unwanted guests for our computers. Antivirus Protection 2012shows windows detected a couple of viruses in your system. It hides in task manager and bares its essentiality by hijacking your system and displaying many misleading pop-ups. Antivirus Protection 2012 cannot safeguard your computer but bring harm to your system. It is an online hub you will be constantly redirected to because of malware interference. Antivirus Protection 2012 can give you more and more uncomfortable warnings on your computer.Antivirus Protection 2012 delivers its payload through deception, just like the fabled Trojan horse of yore. Antivirus Protection 2012 is annoying virus that does intentional damage to your computer hardware or software. The purposes of the rogue Antivirus Protection 2012 is filthy, nothing runs on the computer except for the website to purchase the product. Your computer it is very slow on and off the internet once infected with Antivirus Protection 2012 malware thing. It is nasty and must be removed completely.
Antivirus Protection 2012 virus is stubborn enough to escape from virus removal tools. Antivirus Protection 2012 slows down your computer; the added load of spyware programs in your system’s memory inevitably leads to sluggish performance, at the very least. In addition, some spyware programs do more than just slow down your system and hijack your computer. It acts as it is legit software. Actually it is a big scam. Many victim users found that they can’t get rid of Antivirus Protection 2012 virus for it can block many programs, stop your internet access. It shows many functions that you can use to remove threats but nothing help. Antivirus programs just cannot keep up to remove any of them. You must remove Antivirus Protection 2012 virus ASAP.
Antivirus Protection 2012 ScreenShot

Antivirus Protection 2012 Manual Removal Instructions
Saturday, 28 January 2012
Remove Abnow.com virus manually, Delete Abnow.com google redirects hijacker
Google redirects to Abnow.com?
Abnow.com browser hijacker is a kind of attack program, you can access the correct site when a user tries to change the browser settings, cause the browser to pop up a warning box when the user presses the OK button, it will be directed to the wrong websites. Typical means of transmission include email attachments, misleading links on websites, and files downloaded from the Internet. With abnow.com nothing runs on the computer except for the website to purchase the product. Once your computer was infected with abnow.com then you cannot run any things. This rerouting will be happening when you click on alerts or scan reports delivered by abnow.com trojan.Aabnow.com virus is stubborn just can be detected by virus removal tool, but won't help and it said that abnow.com is not found on your system. Browser hijacking and the corresponding non-pornographic sites such as Aabnow.com can also cause other computer problems arise. Employees at work may cause browsing pornographic web unemployment; users may access pornographic websites by browsing to the illegal content; or even an individual's social relationships as the impact of pornography sites will be gradually reduced, and so on. Aabnow.com records all your Windows-related activities, including the movement and operation of your mouse. Many victim users found that they can't get rid of abnow.com virus or its associated rogue viruses with their installed antivirus programs. Aabnow.com malware can also give your machine a kind of Trojan horse software installation. It is big problem and you must remove abnow.com virus ASAP.
Aabnow.com Screenshot
Aabnow.com Manual Removal Instructions
Step1: To stop all Aabnow.com processes, press CTRL+ALT+DELETE to open the Windows Task Manager. Click on the "Processes" tab, search for the virus, then right-click it and select "End Process" key.Step2: Remove the Aabnow.com virus from registry editor. Click "Start" button and selecting "Run." Type "regedit" into the box and click "OK." Once the Registry Editor is open, search for the registry keys below:
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Policies\System "DisableTaskMgr" = '1'
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run ".exe"
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run ""
Saturday, 14 January 2012
Cannot remove "Internet Security Guard" Virus?
What is Internet Security Guard? Is your machine infected with"Internet Security Guard"?
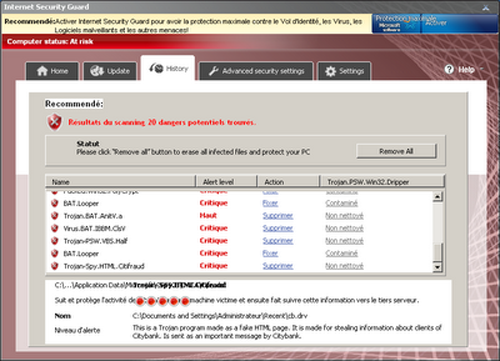
Internet Security Guard is a new released fake antivirus. The present IT world is indeed overwhelmed with plenty of unwanted guests for our computers. Internet Security Guard shows windows detected a couple of viruses in your system. It hides in task manager and bares its essentiality by hijacking your system and displaying many misleading pop-ups. Internet Security Guard cannot safeguard your computer but bring harm to your system. It is an online hub you will be constantly redirected to because of malware interference. Internet Security Guard can give you more and more uncomfortable warnings on your computer.Internet Security Guard delivers its payload through deception, just like the fabled Trojan horse of yore. Internet Security Guard is annoying virus that does intentional damage to your computer hardware or software. The purposes of the rogue Internet Security Guard is filthy, nothing runs on the computer except for the website to purchase the product. Your computer it is very slow on and off the internet once infected with Internet Security Guard malware thing. It is nasty and must be removed completely.
Internet Security Guard virus is stubborn enough to escape from virus removal tools. Internet Security Guard slows down your computer; the added load of spyware programs in your system’s memory inevitably leads to sluggish performance, at the very least. In addition, some spyware programs do more than just slow down your system and hijack your computer. It acts as it is legit software. Actually it is a big scam. Many victim users found that they can’t get rid of Internet Security Guard virus for it can block many programs, stop your internet access. It shows many functions that you can use to remove threats but nothing help. Antivirus programs just cannot keep up to remove any of them. You must remove Internet Security Guard virus ASAP.
Internet Security Guard Screenshot
Internet Security Guard Manual Removal Instructions
Step1: To stop all Internet Security Guard processes, press CTRL+ALT+DELETE to open the Windows Task Manager. Click on the "Processes" tab, search for the virus, then right-click it and select "End Process" key.%Windows%\system32\[random].exe
%Documents and Settings%\[UserName]\Start Menu\Programs\Internet Security Guard\Internet Security Guard.lnk
%Documents and Settings%\[UserName]\Desktop\Internet Security Guard.lnk
Step2: Remove the Internet Security Guard virus from registry editor. Click "Start" button and selecting "Run." Type "regedit" into the box and click "OK." Once the Registry Editor is open, search for the registry keys below:
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\RunOnce “Internet Security Guard”
You can be sure that Internet Security Guard won’t be able to help you protect your computer, for it has no virus detection or removal engine. What it will do is to offer users to buy its activation code to promise you all infections will be gone right away. Keep in mind that is a big scam. The best way to make your PC safety is to completely get rid of Internet Security Guard Virus with PC experts who can assist you to fix it fast and safely.
Thursday, 12 January 2012
Remove Win32/olamrik.tdl4 Trojan Virus - Win32/olamrik.tdl4 Removal Tool
Cannot get rid of Win32/olamrik.tdl4 Completely?
Win32/olamrik.tdl4 is a dangerous MBR infection and your ESET just can detect it. It has disabled comuter user's Internet. With Win32/olamrik.tdl4 nothing runs on the computer except for the website to purchase the product. Once your computer was infected with Win32/olamrik.tdl4 then you cannot run any things. This rerouting will be happening when you click on alerts or scan reports delivered by Win32/olamrik.tdl4 trojan.Users's laptop just started acting weird and they got a lot of pop ups and they did a scan using NOD32 and it stated: "Operating memory - Win32/Olmarik.TDL4 trojan - unable to clean. Como remover can't remove Win32/olamrik.tdl4. It is annoying and must be removed manually. Win32/olamrik.tdl4 virus is stubborn just can be detected by virus removal tool, but won'thelp and it said that Olmarik tdl4 is not found on your system. Many of my files are missing, like movies and word documents. They were not of high importance though, however it would still be good if I can get them back.
Many victim users found that they can't get rid of Win32/olamrik.tdl4 virus or its associated rogue viruses with their installed antivirus programs. One of the victim said "I tried to reboot my PC again and in the process of starting up in Safe Mode all I keep getting was the Blue Screen of Death. I didnt install any hardware or software on my PC so I do not know why I received this BSOD code." It is big problem and you must remove Win32/olamrik.tdl4 virus ASAP.
Friday, 30 December 2011
Remove “System Check” Virus Manually, uninstall fake “System Check”
What is “System Check”?
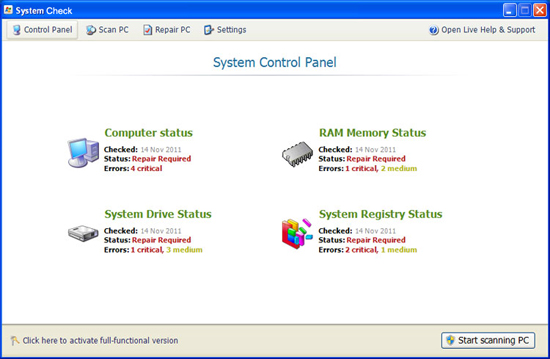
System Check is a fake anti-spyeare software that shows false scan results in order to scare customers into purchasing their rogue program. People have a system check virus on his/her computer and have tried everything to get rid of it and nothing is working. Your infected comp won’t let you do anything it has hide all your files. This fake System Check software is displayed through fake scanner that tells your computer is infected with viruses. Once installed, System Check will start a system scan and report numerous false security threats. System Check is deceptive and aims to lure you to purchase its full version by some fake security reports.System Check rogue program uses scare tactics to convince users that their computers are infected. It blocked your internet and said winsock 2 registry key is missing or could not be accessed. A window popped up called System Check and is scanning. Then an error message says "Windows - delayed write failed. A red X followed by failed to save all the components for the file \\System32\\00006413 or files indexation process failed. The file is corrupted and unreadable. This error may be caused by a computer hardware problem.And still has PC Performance & Stability analysis report fake alert warning. Security alerts and pop-ups add to the alarm and inform the users that they need to purchase the "Registered" version of System Check in order to remove all the "detected" computer threats. System Restore is a malicious scam. So please do not trust System Check Instead of getting rid of System Check Virus immediately.
Keep in mind that System Check is another version of fake antivirus likes the one called System Fix rogue. Once installed, System Check will be configured to start automatically when you start Windows. If you find that your computer is infected with “System Check virus”, please follow the manual removal instructions below to remove System Check from your computer. If you have already purchased this bogus System Check program then you should contact your credit card company and dispute the charges.
System Check Screenshot
System Check Manual Removal Instructions
Step1: To stop all System Check processes, press CTRL+ALT+DELETE to open the Windows Task Manager. Click on the "Processes" tab, search for the virus, then right-click it and select "End Process" key.Step2: Remove the System Check virus from registry editor. Click "Start" button and selecting "Run." Type "regedit" into the box and click "OK." Once the Registry Editor is open, search for the registry key "HKEY_LOCAL_MACHINE\Software\Random." Right-click this registry key and select "Delete."
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer "NoDesktop" = '1'
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Policies\System "DisableTaskMgr" = '1'
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run ".exe" HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "" HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\system "DisableTaskMgr" = '1'
HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Download "CheckExeSignatures" = 'no'
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Explorer\Advanced "Hidden" = '0'
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Explorer\Advanced "ShowSuperHidden" = '0'
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Explorer\ComDlg32\LastVisitedMRU "MRUList"
System Check is created by hackers recently, and is pesky messing up all your files with a black screen. If you thought the System Check virus threat was big, consider the incidence of spyware infection. Or you hesitate to remove yourself for in case due to mistakes damaging your system. The easy way is to get rid of System Check Virus completely with experts who are expert at such issue.
Thursday, 29 December 2011
Remove Mal/FakeAvCn-C Virus manually
Are you annoyed with Mal/FakeAvCn-C?
Mal/FakeAvCn-C is a dangerous Trojan horse detected by Sophos antivirus. If your PC has a Mal/FakeAvCn-C then it has disabled your MS office and plays one of the major parts in this disgusting strategy and you are not easy to terminate Mal/FakeAvCn-C. Mal/FakeAvCn-C is the main process of fake thing that does intentional damage to your computer system. With Mal/FakeAvCn-C nothing runs on the computer except for the website to purchase the product. Once your computer was infected with Mal/FakeAvCn-C then you cannot run any things. Como remover can’t remove Mal/FakeAvCn-C. People recently contracted a virus called Mal/FakeAvCn-C. The computer came preloaded with Windows Security Center, which is turned on but no luck. It is annoying and must be removed manually.Mal/FakeAvCn-C virus is stubborn just can be detected by virus removal tool, but it can’t delete it. Many victim users found that they can’t get rid of Mal/FakeAvCn-C virus with scanner or virus remover. The virus mess up all your files, and devices, such as keyboard, mouse etc. One of the victim said “I tried to reboot my PC again and in the process of starting up in Safe Mode all I keep getting was the Blue Screen of Death... (0x0000007B). I didnt install any hardware or software on my PC so I do not know why I received this BSOD code.” It is big problem and you must get rid of Mal/FakeAvCn-C virus ASAP.
Mal/FakeAvCn-C Manual Removal Instructions
Step1: To stop all Mal/FakeAvCn-C processes, press CTRL+ALT+DELETE to open the Windows Task Manager. Click on the "Processes" tab, search for the virus, then right-click it and select "End Process" key.Step2: Remove the Mal/FakeAvCn-C virus from registry editor. Click "Start" button and selecting "Run." Type "regedit" into the box and click "OK." Once the Registry Editor is open, search for the registry keys below:
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Policies\System "DisableTaskMgr" = '1'
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run ".exe"
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run ""
Wednesday, 28 December 2011
Google Redirects Virus 95p.com Removal Guide
What is 95p.com? Are you annoying browser be redirected to 95p.com?
95p.com (alias http://www.95P.com/search) is a dangerous browser hijacker. 95P.com is represented by rogue antispyware which will control your action on your PC. 95p.com is designed by hackers and they use a couple of viruses to damage your system. When you go to some other web sites, your browser be redirecting to 95p.com. What 95p.com hijacker is applied for is visited by the people whose computers are infected with fake thing. 95p.com bares its essentiality by hijacking your system and displaying many misleading pop-ups. 95p.com hijacker plays one of the major parts in this disgusting strategy. It is an online hub you will be constantly redirected to because of malware interference.95p.com is any type of fishing Ads sites that do intentional damage to your computer hardware or software. The safety scanner said it found it and partially removed it, but nothing has changed on your computer, you still can’t access any programs or open anything just kept redirecting to 95p.com. With 95p.com nothing runs on the computer except for the website to purchase the product that it promotes. Once your computer was infected with 95p.com then you cannot run any things as 95p.com malware is blocking the starting of any program. 95p.com is severe google redirects virus. No antivirus can pick it up both in normal mode and safe mode with networking, it effects IE and Firefox in windows XP, Windows Vista and Windows 7. It is annoying and you must get rid of http://www.95P.com virus immediately.
95p.com ScreenShot
95p.com Manual Removal Instructions
Step1: To stop all 95p.com processes, press CTRL+ALT+DELETE to open the Windows Task Manager. Click on the "Processes" tab, search for the virus, then right-click it and select "End Process" key.Step2: Remove the 95p.com virus from registry editor. Click "Start" button and selecting "Run." Type "regedit" into the box and click "OK." Once the Registry Editor is open, search for the registry keys below:
- HKEY_CURRENT_USER\Software\[random]
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run “[random].exe”
- HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\PhishingFilter “Enabled” = “0″
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings “ProxyOverride” = “”
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings “ProxyServer” = “http=127.0.0.1:33921″
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings “ProxyEnable” = “1″
Needed help removing the 95p.com virus from your computer? Some malicious browser hijacker, such as 95p.com, may offer users to buy it after the victim clicks on a banner or a pop-up while surfing the internet. The best way to make your PC safety is to completely get 95P.com virus removed with experienced experts who are familiar with this annoying problem as soon as possible.
Thursday, 22 December 2011
Hijacked by Mediashifting.com redirect virus? Remove Media shifting trojan manually
Infected with Mediashifting.com Virus?
Mediashifting.com is a pesky hijacker/trojan. It keeps randomly opening tabs in Firefox and directing them to mediashifting.com and other sites of the sort. You ran Anti-Malware but it can't remove the thing even after a reboot, and the same infected file shows up again and again when you run a scan. What mediashifting.com hijacker is applied for is visited by the people whose computers are infected with Click system. Mediashifting.com bares its essentiality by hijacking your system and displaying many misleading pop-ups. Mediashifting.com is deceptive and aims to lure you to purchase what it promotes onsite, it is a scam.
Mediashifting.com is any type of browser hijacker that does intentional damage to your computer hardware or software. With Mediashifting.com you will get that Windows poping up and your explorer/ chrome keep opening tabs to the website mediashifting.com virus and then your computer really running slow. Once your computer was infected with Mediashifting.com,it will shows that Critical Error! Files and programs were infected and files Missing also. Mediashifting.com was copy itself to additional programs and computers, there would be little harm done, save for having all our programs get slightly large. So please remove Media shifting virus ASAP.
Mediashifting.com Screenshot
Mediashifting.com Manual Removal Instructions
Step1: Use anti-virus program to do a full scan and then remove this Mediashifting.com virus once it was detected by the Safeguard program.
Step2: To stop all Mediashifting.com processes, press CTRL+ALT+DELETE to open the Windows Task Manager. Click on the "Processes" tab, search for the virus, then right-click it and select "End Process" key.
Step3: Remove the Protectep.com virus from registry editor. Click "Start" button and selecting "Run." Type "regedit" into the box and click "OK." Once the Registry Editor is open, search for the registry keys below:
HKEY_CURRENT_USER\Software\[random]
HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Download “RunInvalidSignatures” = ’1′
HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\PhishingFilter “Enabled” = ’0′ HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings “ProxyOverride” = ”
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings “ProxyServer” = ‘http=127.0.0.1:59274′
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings “ProxyEnable” = ’1′
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Policies\Associations “LowRiskFileTypes” = ‘.exe’
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run “[random].exe” HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Download “CheckExeSignatures” = ‘no’
Mediashifting.com is indeed a nasty google redirects virus and hard to get rid of. If you thought the virus threat was big, consider the incidence of spyware infection. Or you hesitate to remove yourself for in case due to mistakes damaging your system.The easy way is to get rid of Mediashifting.com Virus completely experts who are familiar with that particular issue.
Saturday, 17 December 2011
American Airlines ticket virus removal, fake American Airlines email virus fix
What is American Airlines ticket virus? Fake american airlines ticket email from American Airlines with an Zip file attachment called aa_ticket.zip spreading from the Internet. Are you in deep water now and trying to get a solution to remove American Airlines ticket virus? Do you feel puzzled that how you get this virus in your computer? Currently, many computer users were suffered from American Airlines ticket virus, one of them said “Well I opened that American airlines email on my mac. I then found out it was a virus on the internet so I deleted everything and was wondering if there was still something I could do to prevent it”. And once you attacked by the American Airlines ticket email scam, all your programs were empty from start menu, and your task manager was blocked, all you get is a black screen. All icons, files and documents were missing. This article will help you know clearly about how to get rid of American Airlines ticket virus safely and permanently.
American Airlines ticket virus is nothing but a fake security tool which can infect a computer by exploiting security vulnerabilities and then mess up your system later. Generally, once you get American Airlines ticket virus in your computer, it will pose a scan automatically showing you fake warnings. With such ignoble scare tactics, the only aim of the producers is to lure you to buy the so called “full version” and then get money from that. Keep in mind that all the viruses and infections are fictitious and the only virus in your computer is American Airlines ticket itself. Don’t fall into this hoax and never pay for it. American Airlines ticket email virus is so tricky that can escape from any security tools. You should remove it manually as soon as possible in case it makes chaos on your computer and damage your system deeply.
Fake American Airlines email message spreads very fast nowadays. The spurious email contains an attached zip file called “AA_Ticket_#5013.zip” including a malicious file named “AA_Ticket.exe” you might notice. American Airlines ticket scam installs rogue software without your permission and disables executable antivirus on your computer. Once it is in your computer, American Airlines ticket malware gives fake warnings to mislead you to pay for it. It can block opening legitimate websites but its purchase page. What’s worse, American Airlines ticket rouge violates your privacy and compromises your security. It will attack your programs and files, block the internet visit, and make your system crash down later if you still leave it in your computer. Please take an action to fix American Airlines ticket problem ASAP.
Step1: In order to end American Airlines ticket virus process, press CTRL+ALT+DELETE to open the Windows Task Manager. Then click on the "Processes" tab, search for the virus, right-click it and select "End Process" key.
Step2: Delete the related files to American Airlines ticket email virus through Registry Edit. Guides to open registry editor, click "Start" menu, hit "Run", then type "regedit" click "OK", while the Registry Editor is open, search and delete the following registry entries listed below:
%AllUsersProfile%\[random]
%LocalAppData%\[random].exe
%Temp%\[random]
%LocalAppData%\[random]
%AppData%\TEMPLATES\[random]
Step 3: Navigate and remove the associated files of American Airlines ticket virus.
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run ".exe"
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings "CertificateRevocation" = '0'
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Policies\Associations "LowRiskFileTypes" =
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Policies\System "DisableTaskMgr" = '1'
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\system "DisableTaskMgr" = '1'
HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Download "CheckExeSignatures" = 'no'
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Explorer\Advanced "Hidden" = '0'
American Airlines ticket virus is really annoying and antivirus programs didn’t pick it up. If you have tried many methods but failed again and again or you haven’t sufficient expertise in dealing with program files, processes, .dll files and registry entries, you can chat with PC experts online 24/7 to completely remove American Airlines ticket email virus from your computer.
American Airlines ticket virus is nothing but a fake security tool which can infect a computer by exploiting security vulnerabilities and then mess up your system later. Generally, once you get American Airlines ticket virus in your computer, it will pose a scan automatically showing you fake warnings. With such ignoble scare tactics, the only aim of the producers is to lure you to buy the so called “full version” and then get money from that. Keep in mind that all the viruses and infections are fictitious and the only virus in your computer is American Airlines ticket itself. Don’t fall into this hoax and never pay for it. American Airlines ticket email virus is so tricky that can escape from any security tools. You should remove it manually as soon as possible in case it makes chaos on your computer and damage your system deeply.
How big is the American Airlines ticket email malware?
Fake American Airlines email message spreads very fast nowadays. The spurious email contains an attached zip file called “AA_Ticket_#5013.zip” including a malicious file named “AA_Ticket.exe” you might notice. American Airlines ticket scam installs rogue software without your permission and disables executable antivirus on your computer. Once it is in your computer, American Airlines ticket malware gives fake warnings to mislead you to pay for it. It can block opening legitimate websites but its purchase page. What’s worse, American Airlines ticket rouge violates your privacy and compromises your security. It will attack your programs and files, block the internet visit, and make your system crash down later if you still leave it in your computer. Please take an action to fix American Airlines ticket problem ASAP.
How to remove American Airlines ticket from my computer completely?
Step1: In order to end American Airlines ticket virus process, press CTRL+ALT+DELETE to open the Windows Task Manager. Then click on the "Processes" tab, search for the virus, right-click it and select "End Process" key.
Step2: Delete the related files to American Airlines ticket email virus through Registry Edit. Guides to open registry editor, click "Start" menu, hit "Run", then type "regedit" click "OK", while the Registry Editor is open, search and delete the following registry entries listed below:
%AllUsersProfile%\[random]
%LocalAppData%\[random].exe
%Temp%\[random]
%LocalAppData%\[random]
%AppData%\TEMPLATES\[random]
Step 3: Navigate and remove the associated files of American Airlines ticket virus.
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run ".exe"
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings "CertificateRevocation" = '0'
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Policies\Associations "LowRiskFileTypes" =
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Policies\System "DisableTaskMgr" = '1'
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\system "DisableTaskMgr" = '1'
HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Download "CheckExeSignatures" = 'no'
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Explorer\Advanced "Hidden" = '0'
American Airlines ticket virus is really annoying and antivirus programs didn’t pick it up. If you have tried many methods but failed again and again or you haven’t sufficient expertise in dealing with program files, processes, .dll files and registry entries, you can chat with PC experts online 24/7 to completely remove American Airlines ticket email virus from your computer.
Remove Strathclyde Police Ukash virus manually
Screen Locked by Strathclyde Police Ukash virus?
Strathclyde Police Ukash virus is nothing but a fake security tool which can infect a computer by exploiting security vulnerabilities and then mess up your system later, to unlock the computer you are obliged, within 48 hours of receiving notice, to pay a fine of £ 100. Generally, once you get Strathclyde Police Ukash virus in your computer, it will lock your PC. With Strathclyde Police Ukash virus, you will need to pay 100 pounds(£
Strathclyde Police Ukash Virus ScreenShot

How dangerous if I leave Strathclyde Police Ukash in my computer?
Strathclyde Police Ukash is a dangerous ransomware. People have encounterd with that “Theres a message come up on my brother's laptop which says its from the met police and says that he's been watching child porn, but its a scam and we can't get rid of it”. Strathclyde Police Ukash installs rogue software without your permission and disables executable antivirus on your computer. Once it is in your computer, Strathclyde Police Ukash gives fake warnings to mislead you to pay for it. It can block opening legitimate websites but its purchase page. What’s worse, Strathclyde Police Ukash virus violates your privacy and compromises your security. It will attack your programs and files, block the internet visit, and make your system crash down later if you still leave it in your computer. Quick to delete Strathclyde Police Ukash virus is required.
Wednesday, 14 December 2011
Fake Security Monitor 2012 virus Removal Tool
How to get rid of Security Monitor 2012 virus manually
Security Monitor 2012 is a fake system security program. Once started, Security Monitor 2012 performs a fake system scan, which also should also convince the user that there is not other way out of the problem. Once installed, Security Monitor 2012 will start a system scan and report numerous false security threats. It shows false scan results in order to scare customers into purchasing it. If your computer was infected with fake Security Monitor 2012 software then it won't let you access yahoo mail. Others have also it seems. If you perform the action then you will be redirected to its so-called legit window to get your money.
Security Monitor 2012 rogue program uses scare tactics to convince users that their computers are infected. It scares you to purchase it in order to remove all the "detected" computer threats. Security Monitor 2012 is nothing else but rogue anti-spyware which has been trying to fool its victims into believing that their computers are infected with malware. Security Monitor 2012 has a wide distribution system which enters even user’s blogging space on the Internet if the access to blogs and journal posts is left public. Rogue Security Monitor 2012 blocks security related programs and websites to protect itself from being removed. It is a malicious scam. You must remove Security Monitor 2012 ASAP.
Security Monitor 2012 ScreenShot

Security Monitor 2012 Manual removal Tips
You can easily and safely eliminate Security Monitor 2012 available online or with the manual removal guide below. This will make sure all the Security Monitor 2012 infections are removed from your computer.
First, you can end it from task manager. Right click Tool bar, select Start Task Manager.
Next, delete the associated files of Security Monitor 2012 in registry editor.
HKCU\Software\Security Monitor 2012
HKCU\Software\Microsoft\Windows\CurrentVersion\Run “Security Monitor 2012″
HKCU\Software\Microsoft\Windows\CurrentVersion\Run “Security Monitor 2012 Security”
HKCU\Software\Microsoft\Windows\CurrentVersion\Uninstall\Security Monitor 2012
Beware of Security Monitor 2012! For it is a nasty virus, and is deeply located in your registry entry, even if you tried to access it in Safe-mode, but the scan would not run and Security Monitor 2012 alert kept popping up. If you thought you don’t have expert skills, you can get instant help from PC experts online to completely get rid of Security Monitor 2012 virus from your PC.
Monday, 12 December 2011
Removing Trojan:DOS/Alureon.E from Win 7
What is Trojan:DOS/Alureon.E?
Trojan:DOS/Alureon.E is a danger Trojan virus detected by Microsoft Security Essentials. You are running Windows 7 system and picked up this trojan last week Trojan:DOS/Alureon.E, but won’t be able to clean it out. What Trojan:DOS/Alureon.E is applied for is visited by the people whose computers are infected with Trojan:DOS/Alureon.E. It can be very malicious indeed. Most of them are intent on controlling your PC. If someone has placed a Trojan on your computer like Trojan:DOS/Alureon.E, they'll be able to see everything that you can. Some of them can even control your webcam. That means the attacker can see you! If you have speakers attached to the PC, they can even hear you! Trying to run Combofix and it will get to the scan mode and stop. The cursor will blink but there is no continuation or completion of the stages.
Many computer users visited some websites and some pop ups asking them to leave or stay came up. After that they started to have a lot of funny things happening like webpage re-directs, music playing randomly through the speakers. The action indicates that they were suffered from Trojan:DOS/Alureon.E. The external drive would not let them turn it off 'remove safely' and they kept getting the message 'drive can not be removed application is accessing'. Trojan:DOS/Alureon.E is associated with some fake programs that does intentional damage to your computer hardware or software. With Trojan:DOS/Alureon.E nothing runs on the computer except for the website to purchase the product. You cannot run any things as Trojan:DOS/Alureon.E malware is blocking the starting of any program. It is annoying and must be removed immediately. You are urgent to protect from Trojans, just because Trojan:DOS/Alureon.E can get onto your PC and mess up your files, makes your computer corrupted although you have Anti-Virus software on your computer. If you have Norton or Mcafee please remember this: Most popular does NOT mean best! Please get rid of Trojan:DOS/Alureon.E virus ASAP.
If you are not sure how to remove the nasty virus Trojan:DOS/Alureon.E. The best way to make your PC safety is to completely remove Trojan:DOS/Alureon.E Virus experienced experts.
Saturday, 10 December 2011
Permanently remove trojan:win32/alureon.tk virus
>What is trojan:win32/alureon.tk?
Trojan:win32/alureon.tk is created by hackers in order to scare customers into purchasing their rogue which will come with trojan:win32/alureon.tk. This trojan:win32/alureon.tk is displayed through MSE antivirus. But antivirus can’t delete it so it keeps coming up on pc tools and you have to reboot. Trojan:win32/alureon.tk is promoted via spam e-mails, malicious or hacked Web pages, peer-to-peer networks.Trojan:win32/alureon.tk uses scare tactics to convince users that their computers are infected. Security alerts and pop-ups add to the alarm and inform the users that they need to purchase the "Registered" version of fake program to remove trojan:win32/alureon.tk from your computer.
Trojan:win32/alureon.tk has a filename that appears to be some type of harmless file, but when you run the file, it’s actually a virus program that proceeds to inflict its damage on your system. Trojan:win32/alureon.tk may block antivirus and antispyware programs that why you will have to ends its processes before installing any removal tool. If you find that your computer is infected with trojan:win32/alureon.tk virus, please follow the removal instructions to completely and manually remove trojan:win32/alureon.tk from Windows XP, Vista Or Windows 7 when you found antivirus programs didn’t work.
What is the best way to remove Trojan:win32/alureon.tk?
If you have performed correctly by following the step by step guide above then you can remove trojan:win32/alureon.tk completely, but if you still scare of the remains of the virus for it mutates every time, you can get assistance from PC Expert online to remove trojan:win32/alureon.tk virus permanently.
Monday, 28 November 2011
Remove Win 7 home security 2012 Virus - How to Get Rid of Win 7 home security 2012 virus permanently?
How did i get Win 7 home security 2012 virus?
Are you in deep water now and trying to get a solution to remove Win 7 home security 2012 virus? Do you feel puzzled that how you get this virus in your computer? This article will help you know clearly about Win 7 home security 2012 virus and give you the safest way to remove it permanently. Quick to delete Win 7 home security 2012 virus is required.
Win 7 home security 2012 virus is nothing but a fake security tool which can infect a computer by exploiting security vulnerabilities and then mess up your system later. Generally, once you get Win 7 home security 2012 virus in your computer, it will pose a scan automatically showing you fake warnings. With such ignoble scare tactics, the only aim of the producers is to lure you to buy the so called “full version” and then get money from that. Keep in mind that all the viruses and infections are fictitious and the only virus in your computer is Win 7 home security 2012 itself. Don’t fall into this hoax and never pay for it. Win 7 home security 2012 is so tricky that can escape from any security tools.
Win 7 home security 2012 installs rogue software without your permission and disables executable antivirus on your computer. Once it is in your computer, Win 7 home security 2012 gives fake warnings to mislead you to pay for it. It can block opening legitimate websites but its purchase page. What’s worse, Win 7 home security 2012 violates your privacy and compromises your security. It attacks your programs and files, block the internet visit, and make your system crash down later if you still leave it in your PC. You should remove Win 7 home security 2012 virus manually as soon as possible in case it makes chaos on your computer and damage your system deeply.
Manually remove Vista Security 2012 Virus
Infected with Vista Security 2012 virus? How to manually get rid of S Vista Security 2012 fake?
Vista Security 2012 is a fake security program released several months ago. You have windows vista and this thing popped out saying you have viruses and you don't want to buy it for you realize that is rogue antispyware software. People have somehow got the fake antivirus program on their computer called Vista Security 2012 and they need to get it off but it won’t allow them to open registry editor. Vista Security 2012 also performs a fake system scan, which also should also convince the user that there is not other way out of the problem. Vista Security 2012 shows false scan results in order to scare customers into purchasing it. Vista Security 2012 installed its self on your computer and it is blocking you from shutting it down in task manager. Vista Security 2012malware may block antivirus and antispyware programs that why you will have to ends its processes before installing any removal tool.You cannot open explorer of chrome on the infected computer for Vista Security 2012 rogue program blocked it. It scares you to purchase it in order to remove all the "detected" computer threats. Vista Security 2012 has a wide distribution system which enters even user’s blogging space on the Internet if the access to blogs and journal posts is left public. You have tried to follow a youtube video to remove Vista Security 2012 from your laptop in windows 7, but no luck. It is a malicious virus and just a big scam. You must remove VistaSecurity 2012 Virus ASAP.
Sunday, 27 November 2011
Win 7 Antispyware 2012 virus? How to remove Win 7 Antispyware 2012 Firewall Alert completely?
What is fake Win 7 Antispyware 2012 Firewall Alert? Are you annoying with Fake Win 7 Antispyware 2012 virus?
Win 7 Antispyware 2012 is a rogue program. Win 7 Antispyware 2012 bares its essentiality by hijacking your system and displaying many misleading pop-ups. What it does is it running like it's looking for spyware or malware and comes up that is found a TON of them. When you ask it to remove it, it charges you for the software. Win 7 Antispyware 2012 is deceptive and aims to lure you to purchase its full version by some fake security reports. This hint seems like support for scammers because you will simply be made to share your money with them. But Win 7 Antispyware 2012 is Fake.
Win 7 Antispyware 2012 is any type of software program that does intentional damage to your computer hardware or software. Win 7 Antispyware 2012 is a rogue application, which means it masks itself with the outlook of some good programs, however, the reality is that it is extremely dangerous. It takes over your screen with its warning alert. The main goal of Win 7 Antispyware 2012 is to persuade you that these detected problems are real, so that you would be scared and finally make the decision to buy this program as the only remedy for removal of all supposedly detected threats. Do not trust these fake promises instead of removing Win 7 Antispyware 2012 Firewall Alert immediately.
Subscribe to:
Posts (Atom)